Delivering an obsolete computer to a recycling facility does not, by itself, establish that its data has been sanitised. Witnessing a prototype being broken apart does not prove that every component was processed correctly or that design information was never copied beforehand. Buyers need answers to three separate questions: Was the correct asset handed over, was the information security outcome appropriately verified, and was the waste handled in accordance with the applicable environmental requirements?
1. Let the asset owner authorise disposal
Start by identifying what will be disposed of and why, before scheduling a vehicle or a guard. IT should assess data-bearing media, the relevant business team should identify prototypes, and legal or compliance personnel should consider retention requirements. Records under investigation or documents that must be retained should not enter a destruction list simply because the device is old.
Use serial numbers or organisational asset identifiers where possible. Define a separate acceptance process for unlabelled boxes, damaged labels and equipment absent from the list. A security officer can record an exception and refer it to the authorised person. That does not make the officer responsible for deciding whether disposal is legally permissible or which technical method is appropriate.
2. Make the custody trail traceable
A useful handover record can identify the authorised parties, date and time, asset or container numbers, visible packaging condition and discrepancies. Bulk weighing may help, but it cannot distinguish different devices of identical weight. For sensitive items, consider whether asset-level records are needed instead of relying solely on a weight receipt.
When a discrepancy appears, determine the item's processing status without treating an employee as guilty. For example, a container may await an authorised decision in an area designated by the operator. This does not confer a right to detain a person without a legal basis. Each change in custody should leave a record that can be explained later.
3. Data sanitisation requires technical verification
NIST SP 800-88 Revision 2 addresses a sanitisation programme using techniques and controls appropriate to information sensitivity. This US technical guidance does not replace Turkish law or mean that one destruction method is suitable for every device.
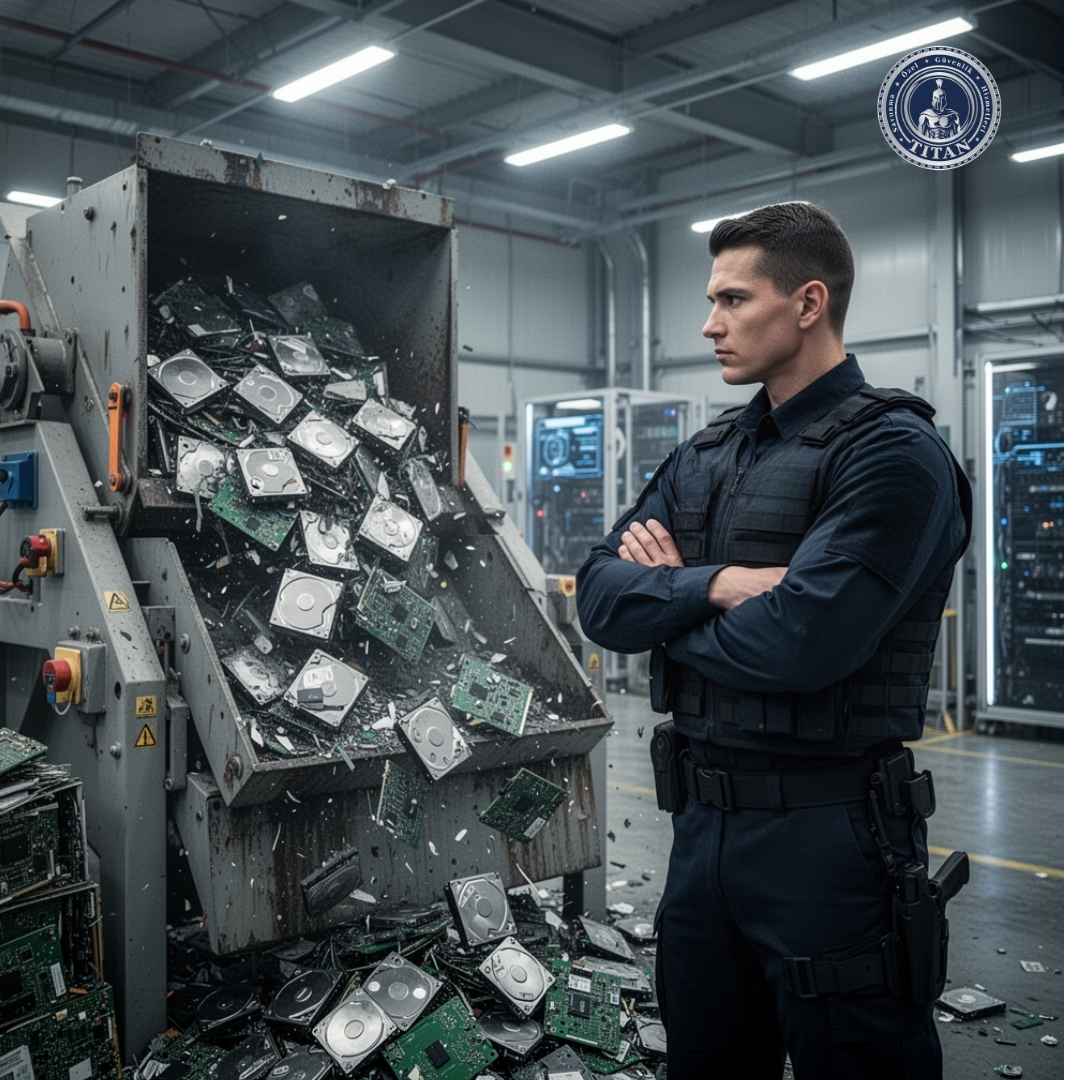
The specification should identify who selects the method, who verifies the outcome and what happens if processing fails. A guard's presence, a video recording or a signature cannot independently establish that data is unrecoverable. Linking a technical report to identifiable assets is more informative than an unspecified batch statement saying “destroyed.” Even when a prototype has no storage medium, its design owner may require separate instructions for components and labels.
4. Check environmental compliance separately
Environmental waste management and information security are distinct checks. The Turkish ministry's announcement concerning electrical and electronic waste describes this as a separate regulatory area. The commissioning organisation should verify the receiving facility's relevant operating scope and required documentation.
Ask prospective providers which document demonstrates which activity, how the custody trail continues through subcontractors, how missing assets or unsuccessful sanitisation are reported, and who can access the final report. This positions guarding as one clearly defined part of the process, with technical data treatment and environmental responsibilities assigned to the appropriate specialists.