An employee leaving an organisation is not, by itself, evidence of violent intent or wrongdoing. Nevertheless, a departure or role change requires decisions about credentials, keys, accounts and company property. In a headquarters or office complex, success depends on timely coordination between HR, IT and building management, rather than security taking over employment decisions.
Separate the employment decision from the access plan
The employer's authorised teams should manage the termination decision and the conversation with the employee. Security usually needs to know which permissions change, when the change takes effect and whom to contact. It does not necessarily need the full history of a personal dispute. Performance or health information should not be copied unnecessarily into security records.
Any concrete threat or violence report requires its own competent assessment. Treating everyone dismissed from a job as aggressive is not a risk assessment. Reports should describe relevant observed behaviour, timing and circumstances rather than attaching labels to the individual.
Account for each separate access system
Building credentials, parking access, physical keys, shared lockers and IT accounts may have different owners. Identify an approving person, an effective time and a completion check for each. The narrow, useful principle in NPSA's guidance is that access should be appropriately removed when people leave or change roles.
Do not assume an action in HR software closes every door permission and account simultaneously. If integration exists, test its coverage and failure handling. If the former employee needs to return for belongings or documents, approve that visit separately rather than keeping old permissions active for convenience.
Make property return a clear handover
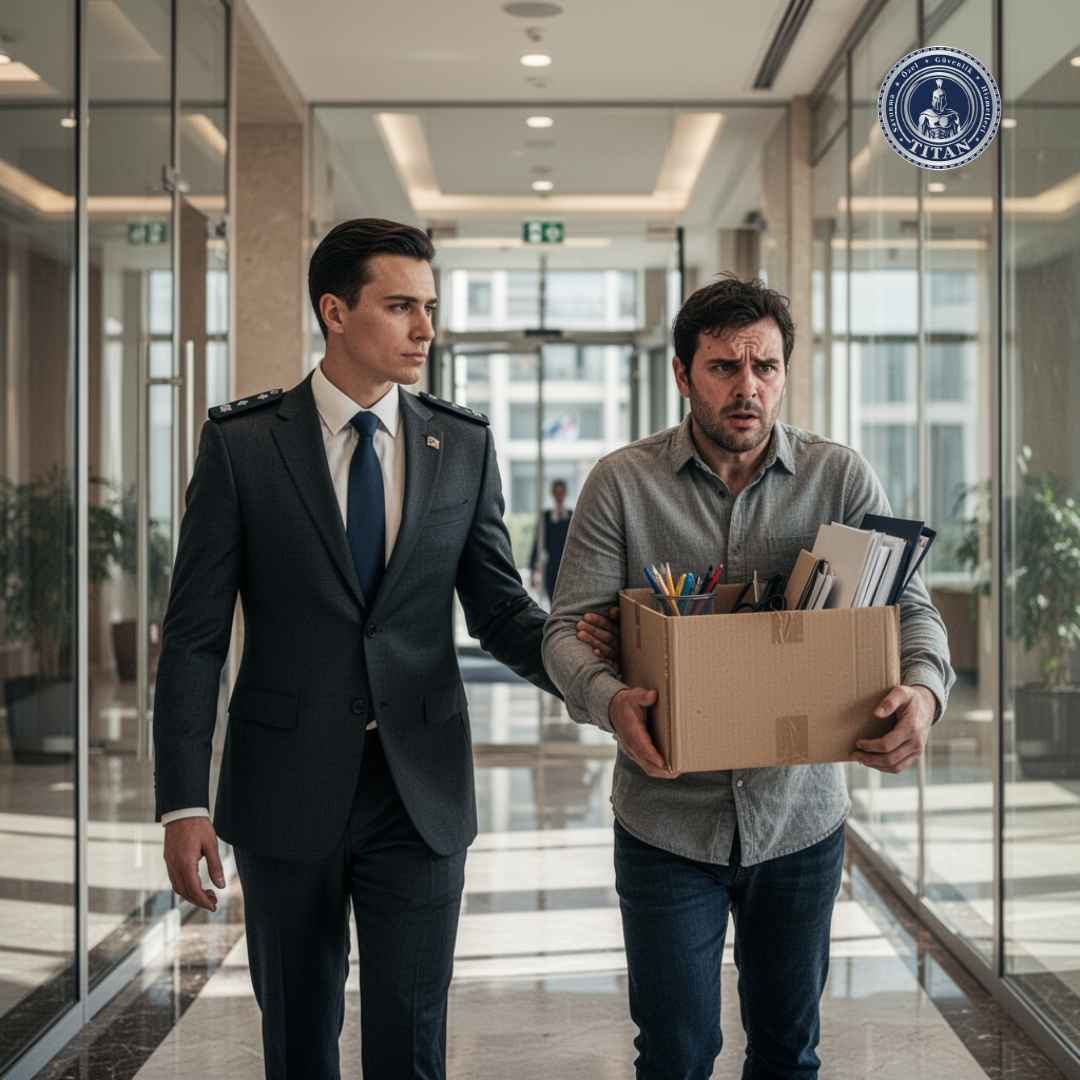
Agree how company property will be returned and personal belongings collected. Who accepts a device, who assesses a missing item and who resolves a disagreement about ownership? An officer should not become the person who independently adjudicates the employer's property claim or searches private files.
If accompaniment is required, its purpose, extent and manner should be proportionate. The aim is not to embarrass the person in front of colleagues. An ordinary departure should not be presented as a covert operation or a force scenario. Any private security intervention remains subject to the applicable legal conditions.
Handle threats through a separate incident process
A threatening incident should activate the workplace's reporting and emergency arrangements. Identify the responsible manager, the person contacting competent public authorities and the person giving staff verified information. A generic instruction to use the same physical intervention or lock down the same area in every incident is inappropriate. Access restrictions must not remove emergency escape options.
After an incident, authorised people should review the necessary records and prevent unnecessary circulation. A former employment relationship should not become a permanent, informally circulated blacklist. Retention and disclosure decisions need an appropriate legal assessment as well as an operational purpose.
Ask a provider to demonstrate the coordination
Walk through an example from the HR notification to confirmation that the final credential has been changed. Who notices a delay? Who corrects access removed from the wrong person? What is passed to the next shift? A useful service plan provides calm, verifiable answers.
This makes offboarding a controlled administrative and security process while preserving dignity. Neither treating all former employees as threats nor promising instantaneous automation can replace an agreed allocation of responsibilities.